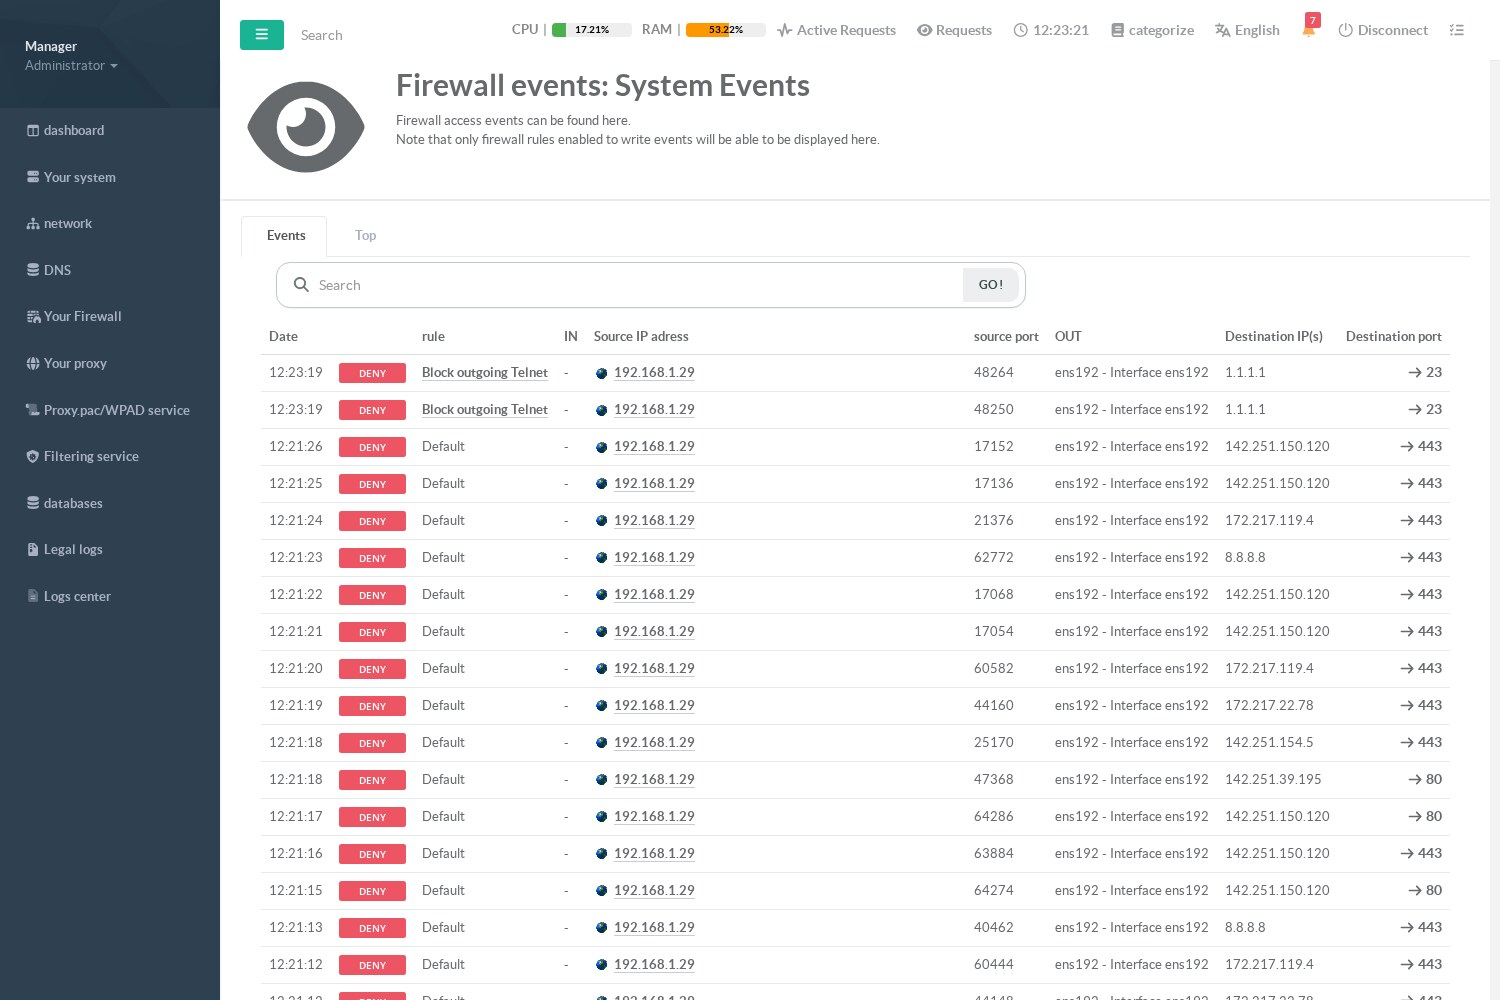
The firewall writes its events to the kernel log. Artica collects them into
/var/log/firewall.logand displays them in Your Firewall › Events.
¶ Which events are logged
Only some packets are written, to keep the log readable:
| Event | When | Shown as |
|---|---|---|
| Rejected packets | Always: every packet rejected by a Drop rule, by a Finally deny all policy (incoming or outgoing) or by the Anti-DDoS connection limits is logged (at most 1 line per second, bursts of 5). | DENY, with the name of the Drop rule, or Default for a policy or the Anti-DDoS limits |
| Log only rules | Every packet matching a rule whose action is Log only (at most 1 line per second per rule). | LOG, with the name of the rule |
| Rules with Log All Events | Every packet matching a rule whose Log All Events option is checked, before its action is applied. | The action of the rule, with its name |
| Log all events (global option) | Every packet accepted or rejected by a rule or a policy, on every interface. See Parameters. | PASS / DENY |
| Transit | Traffic crossing the appliance between two interfaces without a connector, when the transit policy is Reject. | DENY, Transit |
| Connection limits | Connections refused by the limits of a rule that has Log All Events checked. | DENY, LIMIT and the name of the rule |
| Automatic bans | Once per banned source, when the automatic blocking bans it. | Banned automatically |
| Port scans | On an interface linked to the firewall, packets with impossible TCP flags (XMAS, NULL and FIN scans), at most 3 per minute. | Scanner |
A packet rejected by a Drop rule shows the name of that rule; click it to open the rule. Default means the packet was rejected by the policy of the interface or by the Anti-DDoS limits.
¶ Banned addresses
The Banned tab lists the addresses currently banned by the automatic blocking, with their country, host name and remaining time, and an Unban button.
¶ Top: the most active rules, sources and ports
The Top tab ranks the events of the last hour, 24 hours or 7 days:
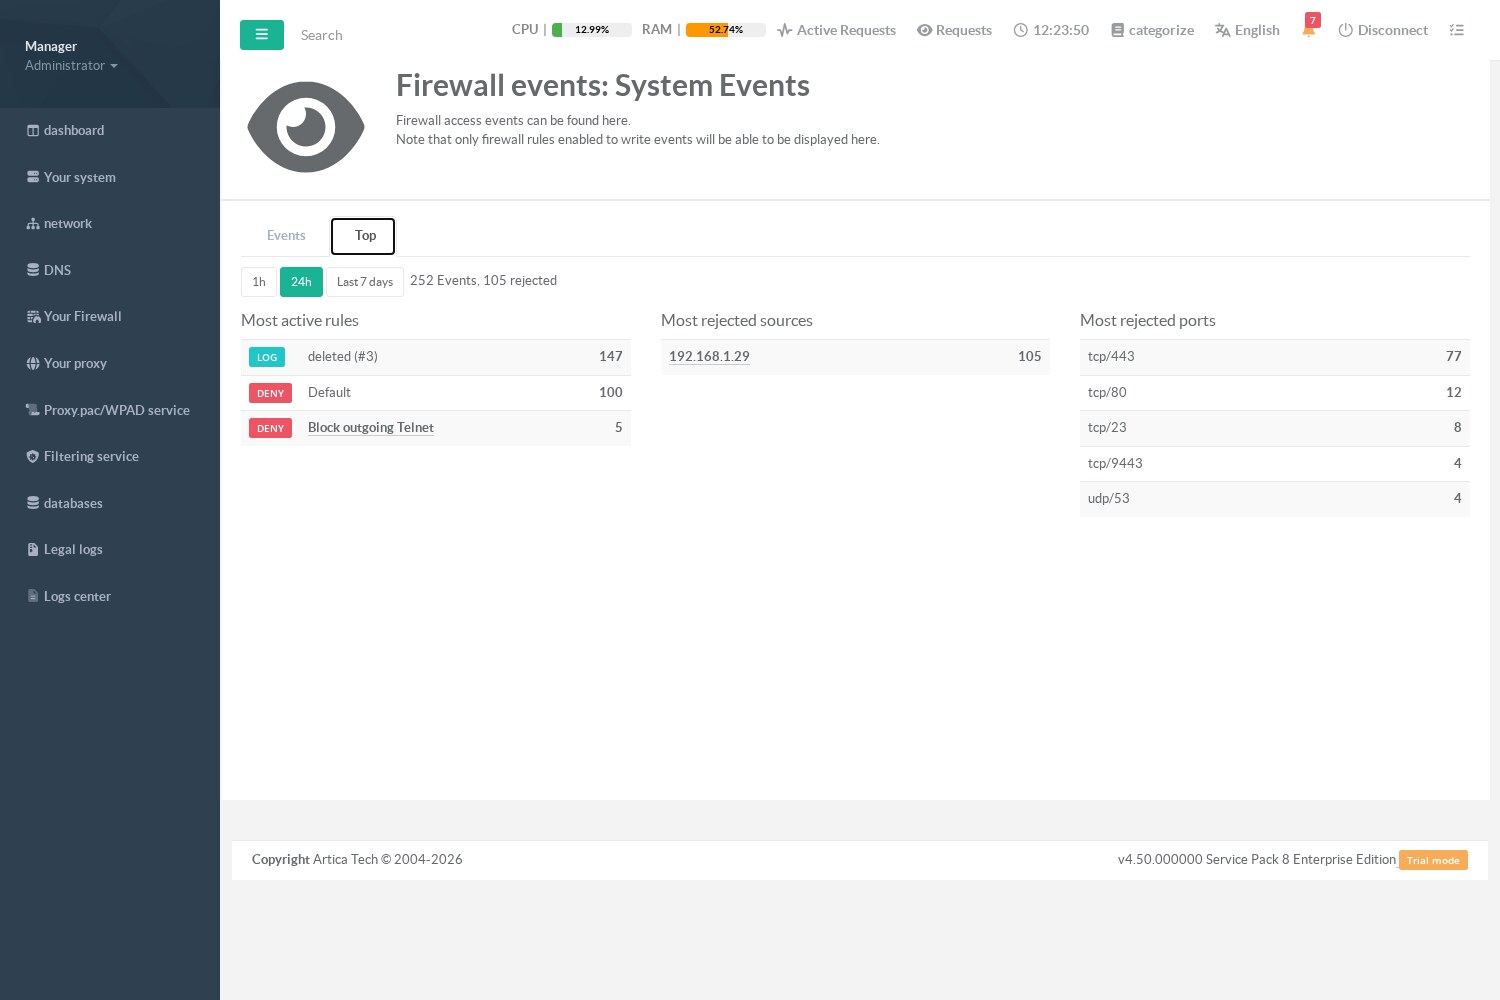
- Most active rules: the Drop and Log only rules that logged the most packets, and the rejections by the policies (Default).
- Most rejected sources: the addresses whose packets were rejected the most — a scanner, a misconfigured device, or a computer that the outgoing policy blocks.
- Most rejected ports: the protocols and destination ports rejected the most; a port at the top of this list often reveals a service you forgot to allow.
The ranking is computed from the event log, so it only counts what is logged (see above) and stays empty when Do not store events locally is on.
¶ Read the table
- IN / OUT: the interface the packet came from or left by. Traffic of the appliance itself has no IN interface.
- Source IP address: click it to see what Artica knows about this address.
- source port / Destination port: empty (
-) for protocols without ports, such as ICMP (ping). - The search field filters the lines (address, port, rule name…).
¶ Example: observe a flow before blocking it
- Create a rule with the action Log only, for example on the service dns, with Outgoing Rule checked to see the DNS queries the appliance sends.
- Open Events: each query appears with the LOG label and the name of the rule.
- When you know which servers are used, replace the rule by Accept and Drop rules.
¶ Storage and forwarding
- Events are kept in
/var/log/firewall.log. When the file exceeds the size set in Export log if size exceed (100 MB by default), it is emptied. - Backup Firewall events (Parameters): before being emptied, the file is copied to the log rotation directory, so no event is lost.
- Do not store events locally: events are only forwarded to the remote syslog servers and to the SIEM, and the Events page stays empty.
¶ From the command line
# Last events
tail -f /var/log/firewall.log

# Rejections only
grep "ARTICA:REJECT:" /var/log/firewall.log

# Events of the "Log only" rule number 3
grep "ARTICA:LOG:3:" /var/log/firewall.logLog prefixes: ARTICA:REJECT:<rule id>: for rejections by a Drop rule, ARTICA:REJECT: for the other rejections, ARTICA:LOG:<rule id>: for Log only rules, FIREHOL:… for the other events (rules with Log All Events, policies, port scans).
¶ No events?
- Traffic from the trusted networks is accepted before the interface rules: it never reaches a Log only rule of an interface.
- Check that the rule is Active and that its Packets counter increases.
- Check that Do not store events locally is off.