Open Status.
Click Modify in Update listener.
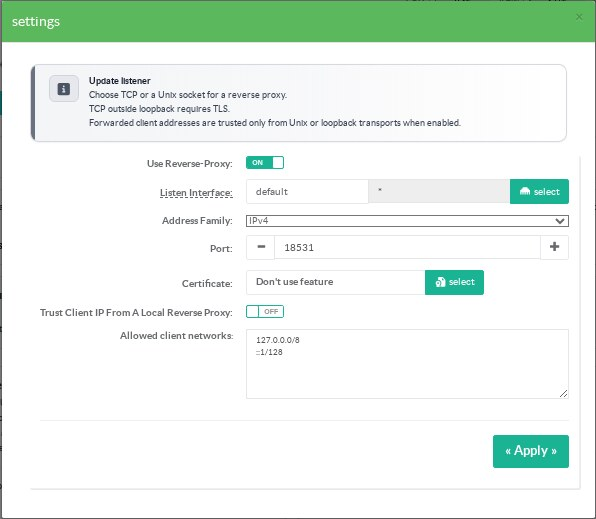
¶ Choose the connection mode
| Setting | Result |
|---|---|
| Use Reverse-Proxy: on | Artica listens on its fixed Unix socket. The widget reads Served by the reverse proxy. |
| Use Reverse-Proxy: off | Artica listens on TCP. The widget displays http://servername:port or https://servername:port. |
The widget uses the appliance host name and the configured port.
Confirm that clients can resolve that name.
With a reverse proxy, use the public HTTPS name of that reverse proxy on Windows clients.
The Unix socket path is managed by Artica and cannot be edited in this form.
¶ Direct TCP access
- Turn Use Reverse-Proxy off.
- Select the listening interface.
An empty or unconfigured selection means all interfaces, shown as*. - Choose IPv4 or IPv6 and set the port.
The default port is18531. - Select a certificate from the certificate centre.
- Add the client subnets to Allowed client networks, one CIDR per line.
- Apply the settings.
Confirm that the service is active and the desired revision matches the applied revision.
TCP listening outside loopback requires TLS.
An interface of * uses 0.0.0.0 for IPv4 or :: for IPv6.
A specific interface uses an address from that interface.
The selected certificate must have its private key and a name trusted by the clients.
An HTTP URL in the widget describes a configuration without a certificate.
It does not override the TLS requirement for a non-loopback TCP listener.
¶ Client address and network checks
Forwarded client addresses are trusted only from Unix or loopback connections when the trust option is enabled.
External TCP clients cannot replace their address with a header.
A CIDR allowlist restricts network access.
It does not authenticate individual computers.
Start with the pilot subnet and a private firewall rule.
Do not expose this experimental listener to the public Internet.